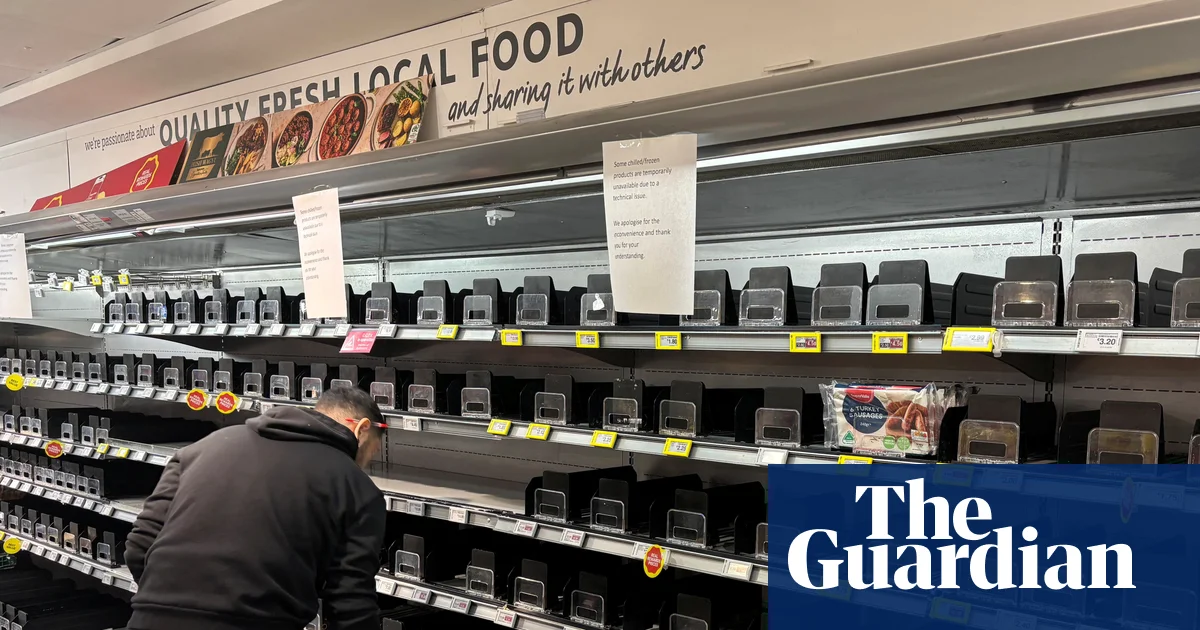
Food suppliers in the UK have been affected by cyber-attacks following incidents in which hackers altered the temperatures of supermarket refrigeration systems across Europe. National Cyber Security Centre (NCSC) director of operations Paul Chichester said the organisation was working with affected companies and that the national impact was minimal. No UK grocery chain had been directly affected at the time of the report.
Retailers in Belgium, Estonia, Finland, Ireland, Luxembourg, the Netherlands and Sweden reported refrigeration problems on Monday, with some temperatures reaching 50C. Several companies confirmed that they had been hacked, while similar incidents were reported in France last month. Investigations indicated that the French supermarket refrigeration systems used legacy technology connected to the internet with default passwords. The NCSC said the attacks were not AI-enabled and had exploited vulnerabilities that had been available for a long period.
British Association of Independent Meat Suppliers said some of its more than 300 members had been affected. The association said no meat had been lost, although one company reported cold units reaching up to 100C and another two had begun defrosting. The affected units were empty. A fruit and vegetable wholesaler in London prevented the attack from escalating by disconnecting its cold-storage units from the internet.
Langridge Organic managing director Alex Pearce said hackers had changed the settings of several units to defrost for more than four hours at 150C, but staff intervened before stock was damaged. Langridge uses the same fridge control system, developed by Copeland, that was involved in the French supermarket incidents.
Cybersecurity researchers reported that attacks on dummy Danfoss fridge controls resembled recent operations linked to Russia. Lupovis chief executive Xavier Bellekens said the firm recorded 256 attempted attacks from 91 different sources between 20 October and 30 October. Most attempts used the manufacturer’s publicly documented factory-default username and password credentials. Bellekens said the attackers remained anonymous, but the infrastructure used for probing had previously been associated with Russian-linked malicious operations.
Kaynak: The Guardian World